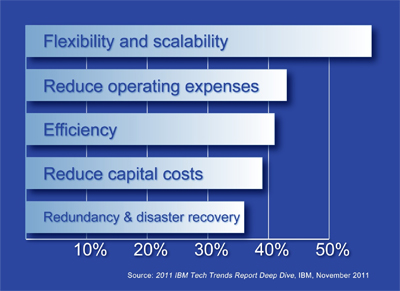
As 2012 begins to wind down, we at Quest are finding that interest in Cloud computing continues to wind up. Our experience is borne out by recent research , which indicates that the business drivers for Cloud computing haven’t shifted much. Here’s a chart from North Bridge Venture Partners’ 2012 report :
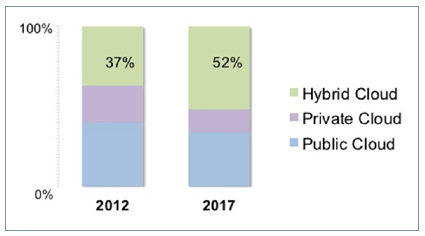
As anyone who does business with smaller enterprises knows, most have begun to use some sort of cloud service. One survey conducted last summer for EMC shows 62% using cloud — up from 28% a year earlier.
Note that most of these companies are using public cloud services, and plenty of that use is what’s called ‘shadow IT’ — which is to say, end-users are doing unauthorized end runs around their IT departments to access these public cloud services for the sake of convenience and ease of use.
A recent report by Forrester Consulting suggests your web applications may be far more vulnerable than you think. According to Forrester, 51% of the 240 North American and European companies surveyed experienced at least one application security incident since the beginning of 2011. And 18% of those suffered losses of at least $500,000. For 8% of those surveyed, losses topped $1 million.
The majority of developers are not security experts, and secure coding is historically not identified as a priority. Oftentimes, the arduous task of vulnerability identification and remediation cannot be successfully addressed by limited IT security resources.
Look for an app development services provider who offers a time-saving solution for all types of security testing — outsourced, individual, and enterprise-wide analysis — and for all types of users, including application developers, build managers, Quality Assurance (QA) teams, penetration testers, security auditors, and senior management.
Last time , I looked at some of the security issues related to employee mobility, which focused mainly on devices like smartphones and tablets and how people use them.
But smartphones and tablets aren’t the only mobile devices business leaders need to worry about. Consider:
USB malware is gaining momentum — so flash drives and other USB-connected devices can become malware vectors.
Hackable RFID and radio frequency channels create voicemail vulnerabilities and enable call interception.
RAM scraping exploits moments when sensitive encrypted data is unencrypted in browsers, smartphones, point-of-sale system memory, etc.
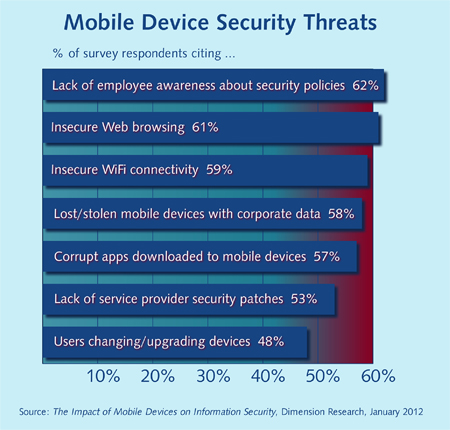
Late last year, market researcher IDC reported that by 2015 more U.S. Internet users will access the Internet through mobile devices than through PCs or other wireline devices. Judging by the eager embrace of smartphone and tablets since then, I’d guess their prediction may be conservative.
And unquestionably, this kind of mobility in business is a game-changer both in terms of how we do business and how we do information security.